TECH
What eMudhra’s security breach means
Private keys associated with eMudhra’s eight intermediate certificates have been compromised; could allow malicious actors to impersonate websites and intercept secure connections.
Private keys associated with eMudhra’s eight intermediate certificates have been compromised; could allow malicious actors to impersonate websites and intercept secure connections.
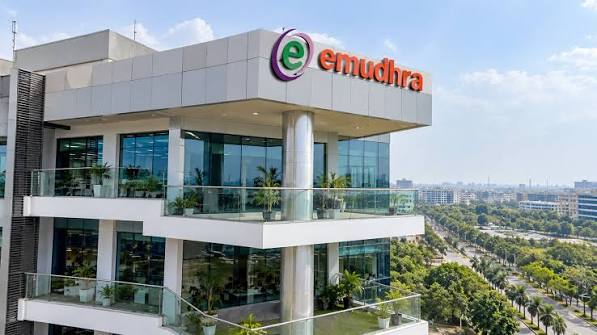
Indian digital certification authority eMudhra has disclosed that private keys associated with its eight intermediate certificates have been compromised, meaning that more than 60 million certs it has issued can’t be trusted and needs a massive clean-up exercise.
Alarm bells have been raised that these keys could be exploited by malicious actors to impersonate websites and intercept secure connections.
“On Saturday, October 17, at 20:06 UTC, Mozilla received a report from a community member that private keys associated with eight eMudhra intermediate certificates had been compromised,” wrote Dennis Jackson, a member of Mozilla’s cryptography engineering team.. “These keys could allow attackers to issue fraudulent HTTPS certificates for websites they do not control.”
An independent researcher flagged the security risk to major browser companies such as Apple, Google, Microsoft and Mozilla who have since blocked all eight of the intermediate certificates in question.
eMudhra, a Bengaluru-based tech company which issues certificates for digital signatures that are used by browsers to authenticate websites, said in a statement that the incident has no connection with its Indian Digital Signature Certificate (DSC) and eSign businesses but affected a small part of global TLS (Transport Layer Security) business.
TLS certificates, popularly associated with HTTPS websites, are a set of security protocols that ensure data transmission among digital assets, like browsers and apps, in a secure manner.
"eMudhra Ltd, an India-based Certification Authority (CA), has reported a compromise of private keys associated with eight intermediate CA certificates in its public key infrastructure (PKI), comprising six TLS certificates and two code-signing certificates," the CERT-In note said.
PKI consists of several components, including public and private keys, for digital assets in mathematical codes used for encryption, digital certificates issued to websites as a mark of trust, etc.
The compromised keys can be used by cyber criminals to develop a fraudulent online platform impersonating any genuine payment entity and lure people to make payments.
eMudhra said its infrastructure was not compromised, no data was breached, and all physical and logical security controls of the firm remained intact.
"The affected global TLS business is a very small part of eMudhra's operations and accounts for around 1% cent of the company's revenue. However, this may have some reputational risks for eMudhra, which cannot be quantified.
"eMudhra is working directly with customers who may be affected to give them replacement certificates, so that critical services are not disrupted. The company is also working with the root programs and continues its root-cause investigation," eMudhra said.
The IT Ministry has issued a statement emphasising the separation between eMudhra’s two service areas. “The second function [eMudhra’s TLS business] is international in nature and operates under a global trust framework. It is governed by international standards and subject to independent audits, including WebTrust audits conducted by BDO International Limited,” the ministry said.
“The reported security incident pertains to this only. MeitY is not involved in its audit. The impact of this incident on Indian websites and applications have been very limited and for a very short interval,” it said, adding that a special team has been constituted to investigate the matter.
eMudhra said a flaw in its system led to the creation of a set of weak keys alongside the original strong keys. A researcher had reported to Apple, Google, Microsoft and Mozilla that the weak keys could be reverse-engineered possibly with AI-assisted techniques.
"An attacker possessing these private keys could issue fraudulent certificates for domains they do not control. Such TLS certificates could be used to impersonate legitimate websites and facilitate man-in-the-middle (MitM) attacks, potentially enabling the interception or modification of encrypted communications.”
What did Cert-In say
In an advisory issued on Wednesday, the Indian Computer Emergency Response Team (CERT-In) said that the private keys of six TLS certificates and two code-signing certificates were generated with “insufficient cryptographic randomness.”
"The compromised code-signing keys could be used to issue fraudulent code-signing certificates," cybersecurity watchdog Cert-In said.
According to Cert-In, Google has blocked the public keys of the affected TLS intermediates in Chrome through a Certificate Revocation List Set (CRLSet) update.
Google has also announced the removal of emSign ECC Root CA- G3 -- a product of eMudhra, from the Chrome Root Store.
eMudhra's emSign is a global digital trust and PKI platform developed by eMudhra, offering SSL and TLS certificates, email security, code signing, and centralised certificate lifecycle management via emSign Hub
Mozilla blocked the six affected TLS intermediate certificates of eMudhra.
The change is scheduled for release to all devices relying on the Chrome Root Store on 27 October.
eMudhra said it is working directly with customers who may be affected to give them replacement certificates, so that critical services are not disrupted.
The company further said it is working with the root programmes as part of its ongoing investigation of the incident.
SBI’s customer data exposure
The incident coincides with State Bank of India, the country's largest bank, disclosing suspected exposure of 3,897 customer records containing personally identifiable information on the dark web, following alerts it received on 16 October from its threat intelligence service provider.
SBI in a regulatory filing said that a preliminary analysis of around 3.75 lakh records available on the dark web identified 3,897 customer records containing sensitive information, including registered mobile numbers, dates of birth, names, gender, email addresses and residential addresses.
The exposed information reportedly also included branch and Customer Information File (CIF) identifiers, lead IDs, and metadata associated with loan and lead records and other related files.
It said a detailed investigation was required to establish the authenticity and completeness of the exposed data, determine the potential source and extent of the exposure, and assess the associated risks to customers and the bank.